Vexta · Features
Everything Vexta does, in one place.
Vexta maps your attack surface, scans web apps, APIs, networks and mobile binaries, tries to prove each finding before you see it, and writes reports a human can read. One self-hosted engine, from recon to remediation, so the whole workflow lives on hardware you control.
Capabilities
From attack surface to a report you can send.
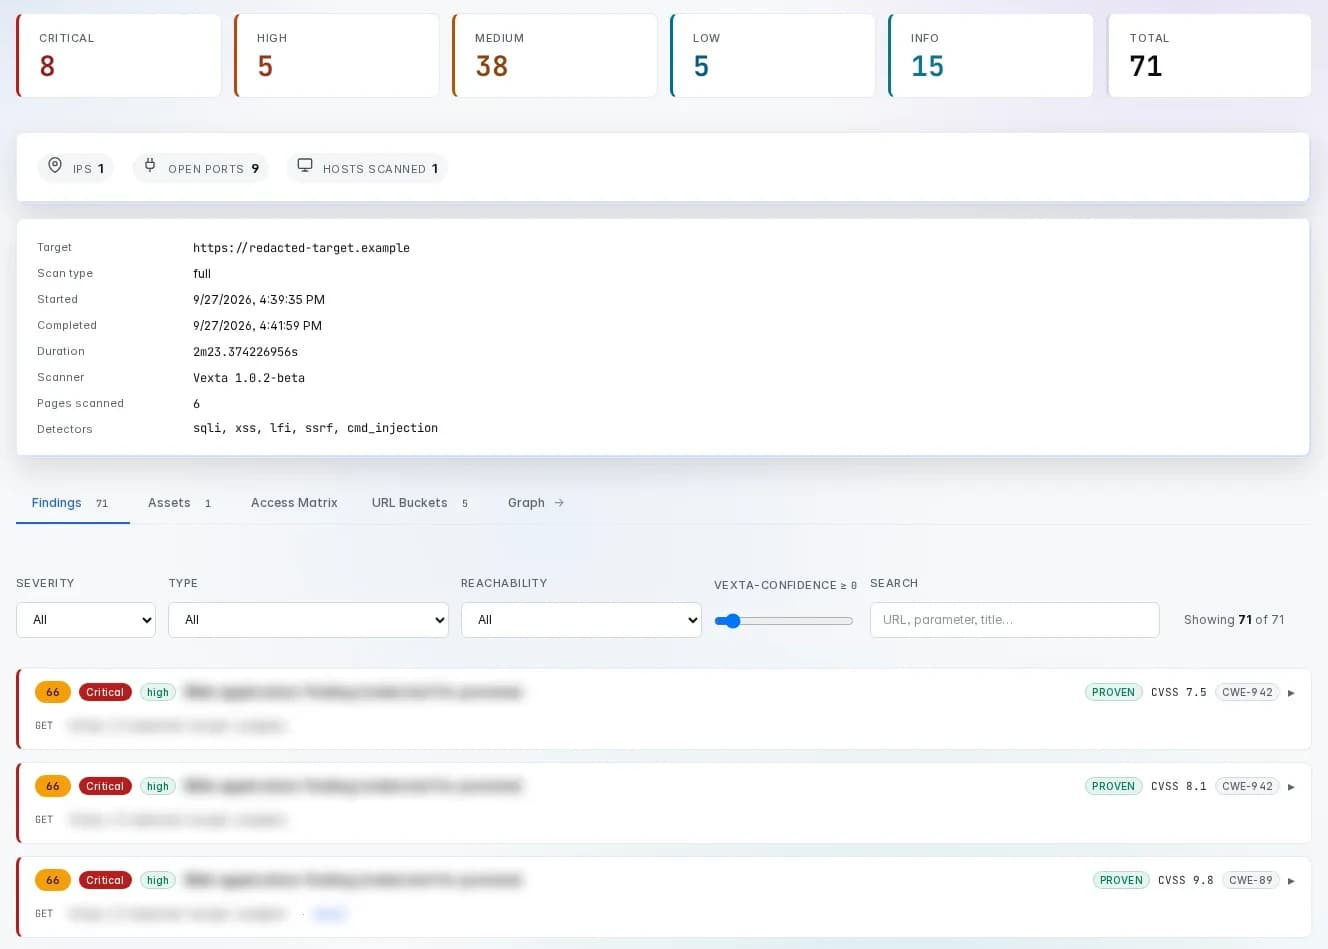
The same engine covers discovery, scanning, verification and reporting, so a finding does not change hands between four tools before anyone can act on it.
Autonomous recon
Vexta maps your attack surface - subdomains, endpoints and technologies from 40+ passive sources plus active discovery - so a scan covers the assets you forgot you had, not just the one URL you typed.
Web & API vulnerability scanning
25+ vulnerability classes, including SQLi, XSS, SSRF, SSTI, XXE, broken access control, request smuggling and GraphQL, with type-aware payloads and dedicated API handling - not just CVE version-matching.
Network scanning
Discover live hosts, open ports and exposed services across a network range, so the infrastructure around an app is in scope too, not an afterthought.
Proof-of-exploitation
A non-destructive verifier tries to safely confirm each candidate finding before you see it. Every finding comes back proven, refuted or unproven, and a network error never turns into a false "refuted".
Vexta Confidence Score
Every finding gets a 0-100 score combining severity, detector confidence and proof status. On Pro and Enterprise it also weighs EPSS probability and CISA KEV status, and asset reachability on Enterprise.
Optional AI triage
With your own Anthropic, OpenAI, Gemini or Azure OpenAI key, an LLM layer adds context and fix guidance and flags likely false positives. It never deletes a finding, and it stays off unless you turn it on.
Mobile app security
Upload an Android APK for static, dependency, native-library and data-flow analysis, with findings mapped to OWASP MASVS and CWE.
Learn more
Bug bounty and authorized scope
Import a program or engagement scope and Vexta enforces it as a strict allow-list on every request. Pro adds the intercepting proxy, PoC generation and export to HackerOne and Bugcrowd.
Learn more
CI/CD and reports
A Word report on every plan. Pro and Enterprise add HTML and PDF reports, SARIF and JUnit output for GitHub, GitLab and Jenkins, and the scan-ci command for pipeline gates.
Discover
Recon that finds the assets you forgot about.
Attackers start with reconnaissance, and so does Vexta. It enumerates subdomains and endpoints using passive sources plus active discovery, building a map of your real attack surface before it scans. The forgotten staging host and the unlinked API are exactly where the exploitable bugs tend to hide.
- Subdomain and endpoint enumeration from 40+ passive sources
- Active discovery to fill in what passive sources miss
- Network host, port and service discovery across a range
- Scope stays enforced throughout, so discovery never wanders out of bounds
Verify
A short, verified list beats a long, unverified one.
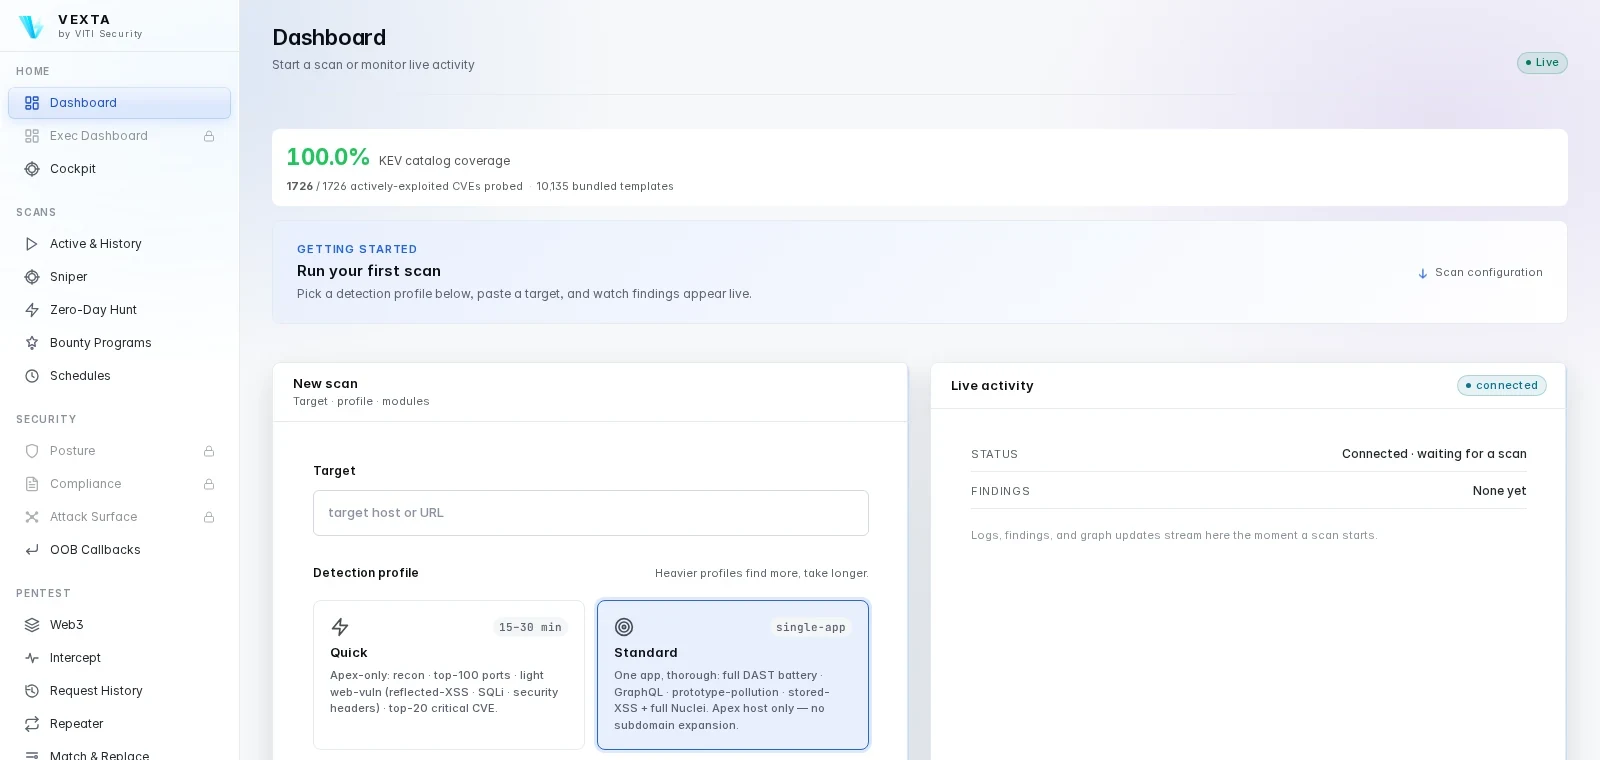
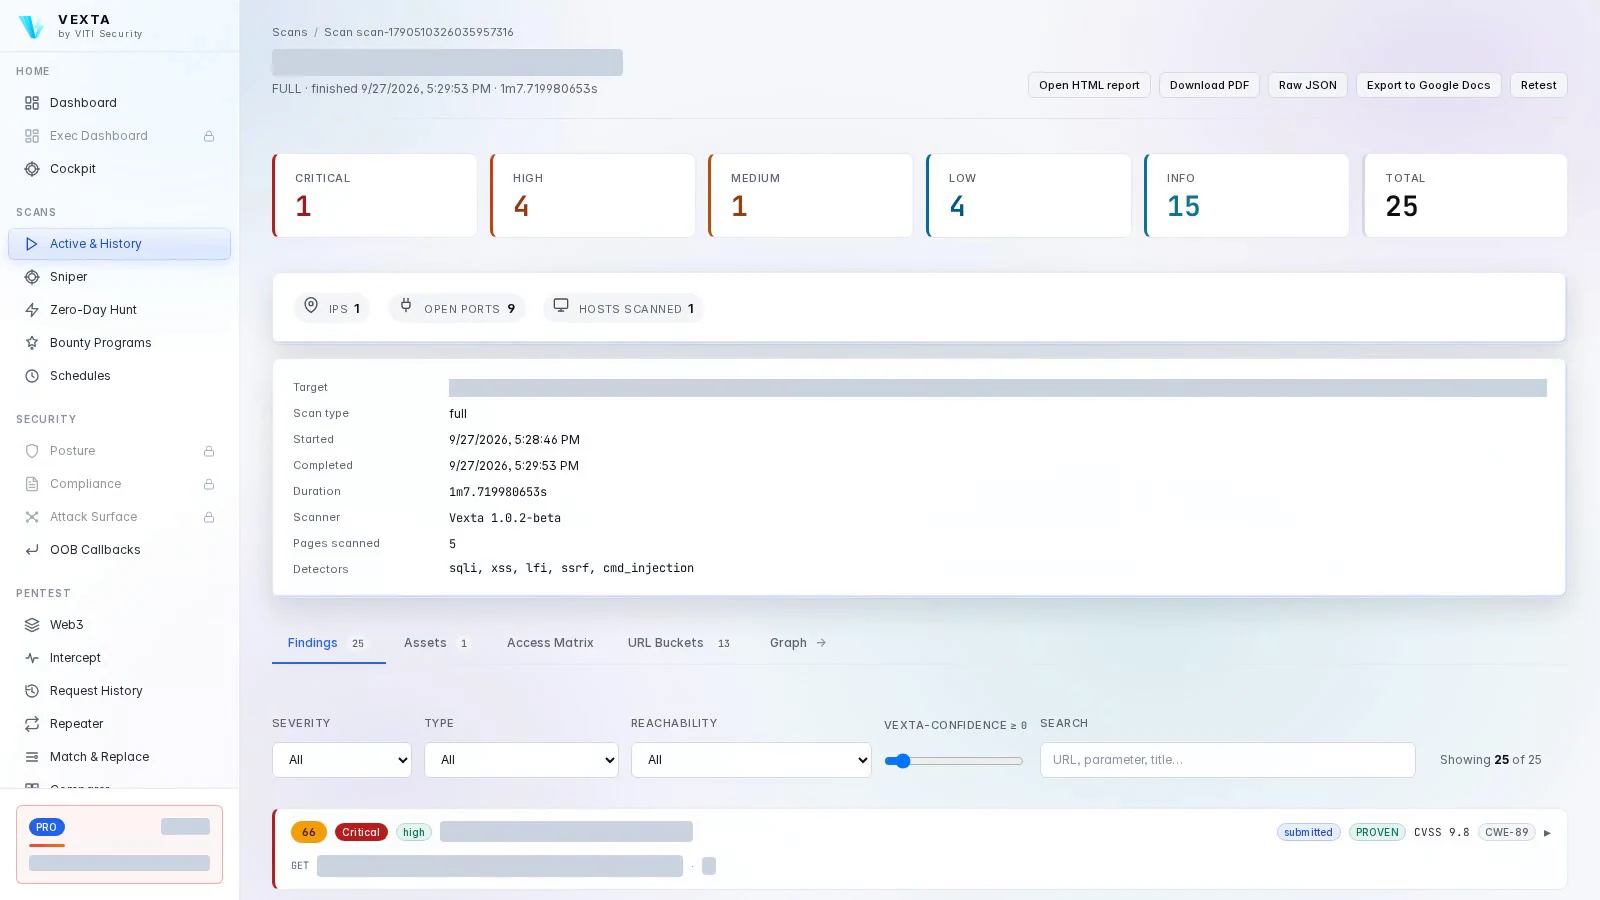
A scanner that matches versions to a CVE feed can hand back hundreds of maybes. Vexta runs each candidate through a non-destructive verifier that tries to safely confirm it, marks it proven, refuted or unproven, and ranks the list by its 0-100 Vexta Confidence Score - so your team starts with the issues that are real.
- Non-destructive verification before a finding reaches you
- Each finding marked proven, refuted or unproven
- A network error never gets recorded as a false all-clear
- Ranked by the 0-100 Vexta Confidence Score
Report
Reports a human can read - and a pipeline can parse.
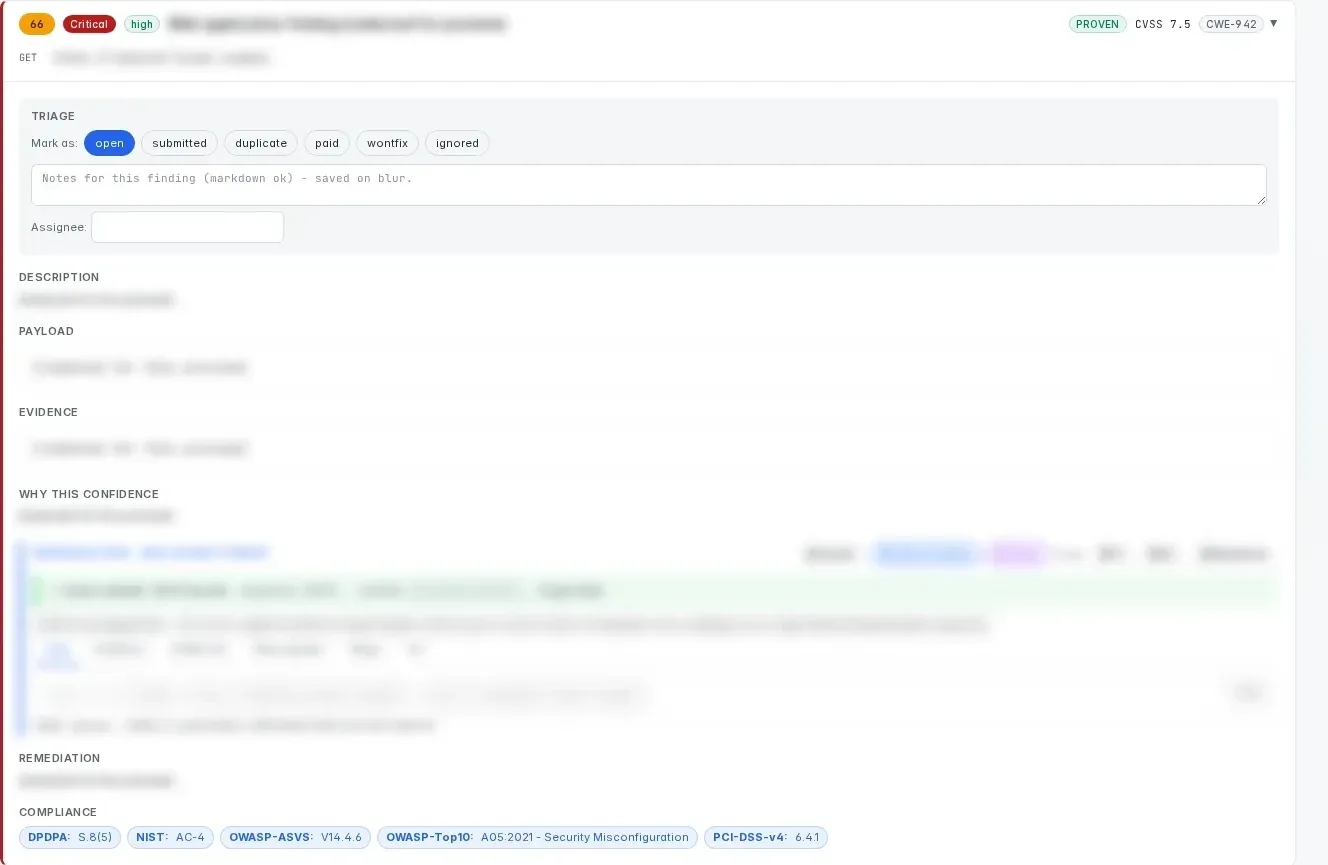
Findings export the way the recipient needs them: a report with an executive summary and remediation steps for a client or an auditor, and machine-readable output for a code-scanning dashboard or a CI gate. No reformatting a raw JSON dump before anyone else can use it.
- A Word report on every plan
- HTML and PDF reports on Pro and Enterprise
- SARIF and JUnit output for CI pipelines on Pro and Enterprise
- Self-hosted as a single binary, so results stay on hardware you control
Under the hood
Vexta features - frequently asked questions
Does Vexta cover more than web applications?
How does Vexta keep the finding list manageable?
What report formats does it produce?
Can I scan a mobile app with it?
How does it stay within an authorized scope?
Where does my scan data live?
See the whole platform on one of your own targets.
Start a free trial and run Vexta end to end, or book a call and we will walk through the capabilities that fit your workflow.