
The pentest report and audit readiness your customers ask for.
We test your apps, cloud and network on a scanner we built ourselves, back every finding with evidence, and help you close each one.
I need security work done
Pentest (VAPT), SOC 2 / ISO 27001 readiness, vCISO, incident response.
Get a quote →I want to run the scanner myself
Vexta: verified findings, self-hosted, your data stays with you.
Start free trial →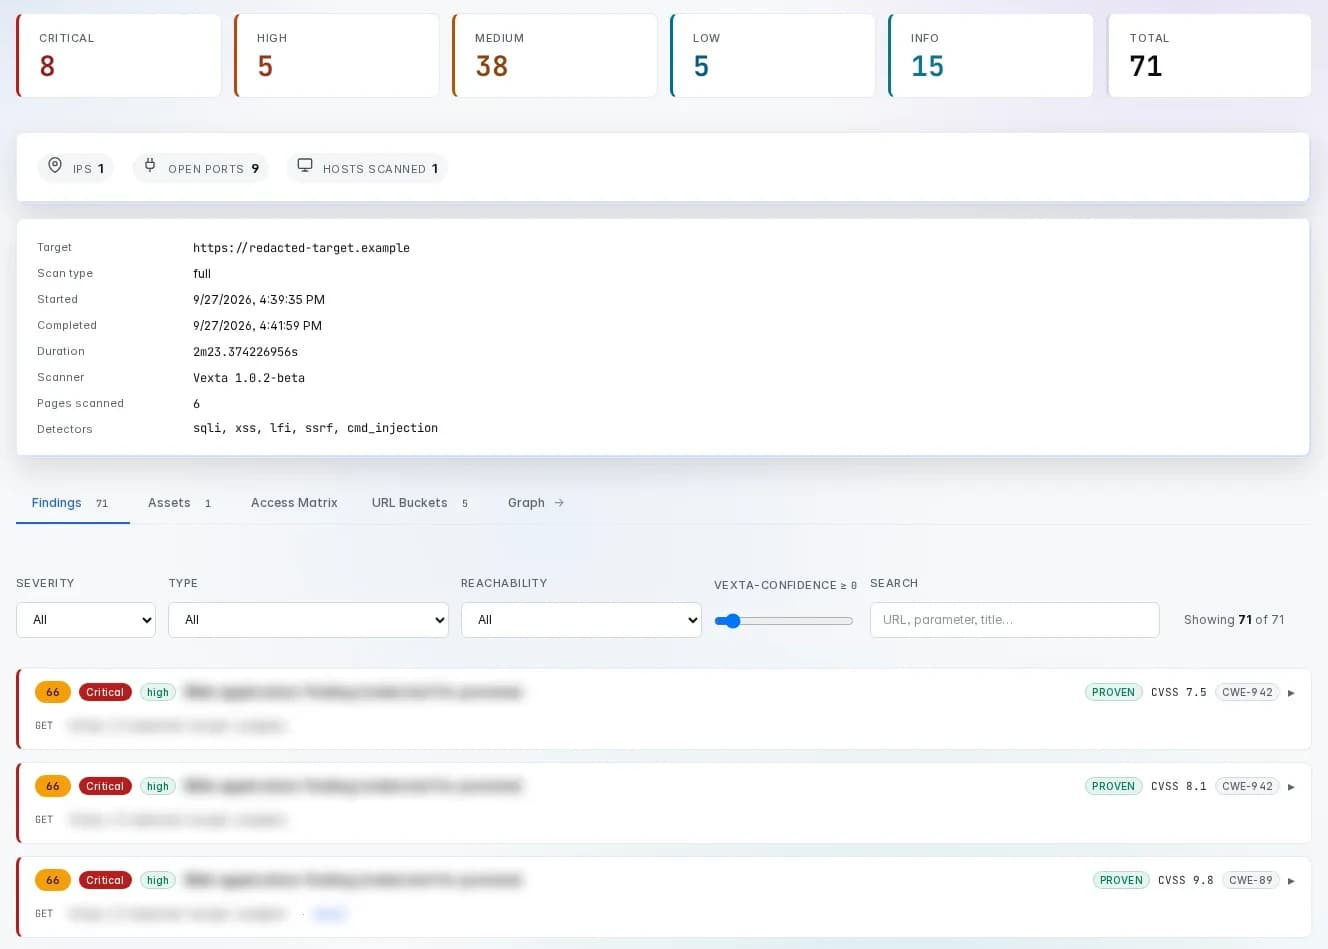
- Founded 2020
- Self-hosted scanner
- 2 wk
- From scoping call to first findings
- 24×7
- Automated monitoring, with a human on call
- 1 business day
- From your requirement to a fixed quote
- 10,000+
- Community detection templates (ProjectDiscovery), checked by our own verifiers
See the deliverable
Read the report before you buy.
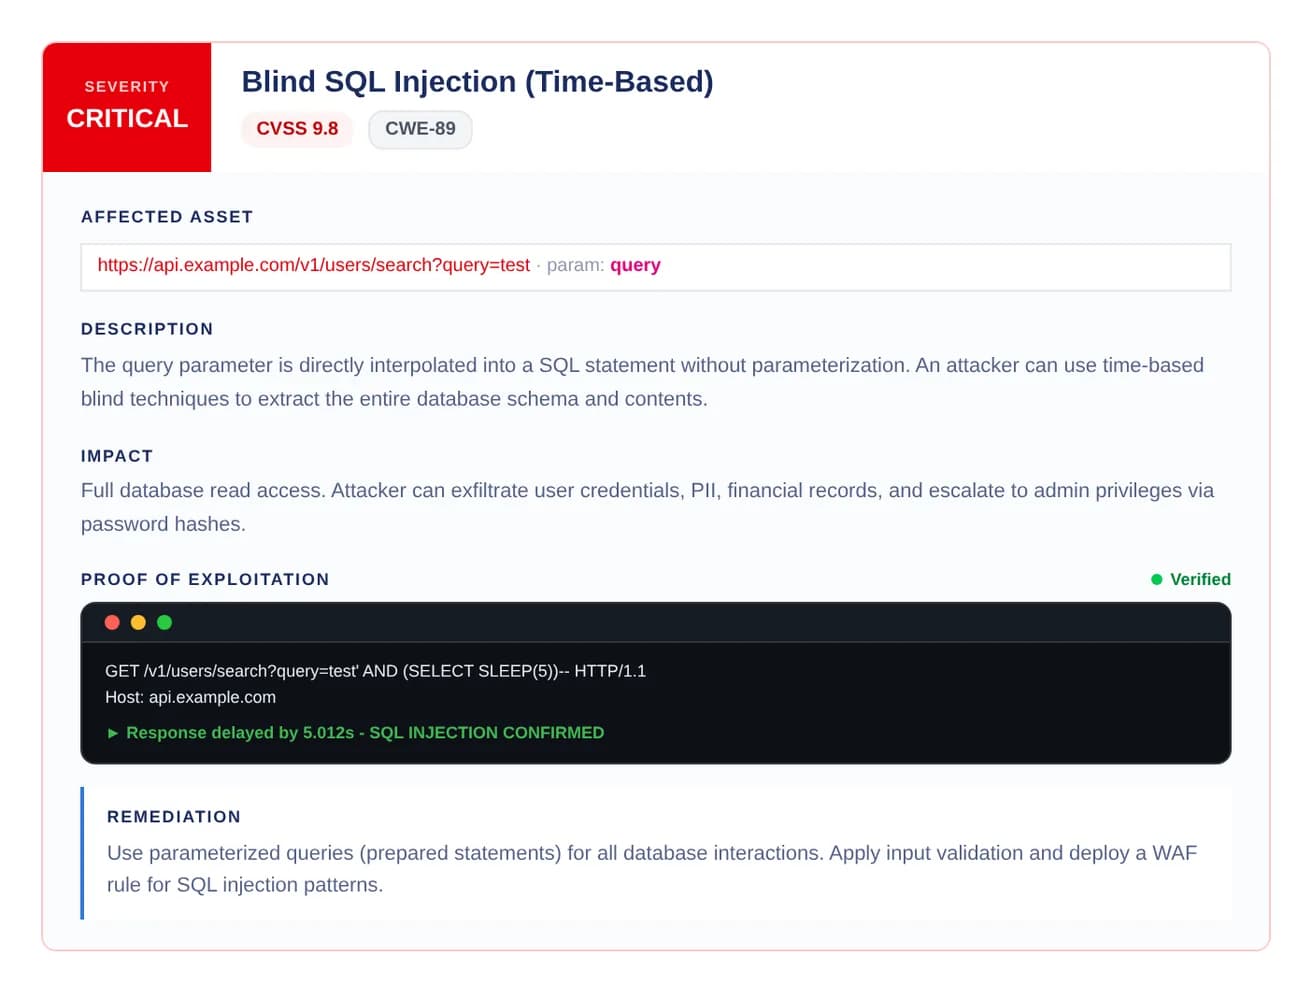
Our sample VAPT report is published in full, not gated behind a form. Your report follows the same structure.
- An executive summary with an overall risk rating
- Every finding ranked, with CVSS and CWE
- The affected endpoint and steps to reproduce it
- A fix for each finding, then a re-test
Our Services
Security first. The IT that supports it, second.
VAPT & Penetration Testing
Exploit-grade testing. OWASP, NIST 800-115, PTES.
Learn moreCybersecurity Services
VAPT, compliance prep, incident response, posture management.
Learn morevCISO Services
A security leader on retainer, without the six-figure hire.
Learn moreManaged IT Services
The IT function behind the security work.
Learn moreCloud Services
AWS, GCP and Azure. We pick what fits.
Learn moreIT Consulting
Strategic planning, vCIO, and audits.
Learn moreWhy VITI
Why the work holds up.
We own the engine
Vexta is ours. When a finding fires we can show you the check that produced it, and adjust that check ourselves.
No licence markup
We are not passing you an enterprise tool subscription with a margin on top. You pay for the testing and the remediation, not for our software bill.
The number is on the website
Retainers and Vexta plans are published. You get a fixed price before work starts, not a quote that drifts.
The same engineer throughout
The person on your kickoff call is the person who does the testing and the re-test. No hand-off from the senior pitch to a junior delivery team.
Industries we serve
Built for the constraints you actually have.
The engine behind the work · Vexta
Every engagement starts with our own scanner.
Vexta is ours. We built it so every finding we report can be traced to the exact check that produced it. It runs before a human writes a single finding, which keeps our reports short and every finding explainable. You can also license it directly.
- Findings are verified before you see them - proven, refuted or unproven, never a maybe
- Ranked by what is actually exploitable on your estate, not by raw CVE count
- We can show you the exact check that produced any finding, because we wrote it
- When a new CVE matters to you, we change the engine rather than wait on a vendor
From the blog
Recent writing from our team.
Nov 16, 2026
Microsoft 365 Outage EX1550543 Phishing Campaign Security Advisory
Microsoft 365 experienced a global outage tracked as EX1550543, which attackers are currently exploiting through targeted credential phishing campaigns.
Read
Nov 16, 2026
Penetration Test vs. Vulnerability Scan: What Your Stakeholders Actually Expect
Understanding the difference between a penetration test and a vulnerability scan is critical for SMBs. Your customers, auditors, and insurers are almost always asking for a full penetration test, not just an automated scan, when they use the term.
Read
Nov 15, 2026
UnrealIRCd CVE-2026-114713 Security Advisory: What SMBs Must Do
CISA added a critical UnrealIRCd vulnerability tracked as CVE-2026-114713 to its KEV catalog after active exploitation. Read our security advisory for SMBs.
Read
Nov 15, 2026
Data Breach at Your Tax Office: The First 48 Hours, IRS Reporting, and Client Notice
If your tax firm suspects a client data breach, immediate action is critical. Learn the essential steps for containment, IRS notification, and client communication within the first 48 hours to mitigate damage and ensure compliance.
Read
Nov 14, 2026
Regulation S-P vs. FTC Safeguards Rule: Which Applies to Your Firm?
For US financial firms, understanding whether Regulation S-P (SEC) or the FTC Safeguards Rule applies hinges directly on your primary regulatory body and the specific nature of your business operations.
Read
Nov 13, 2026
Navigating SOC 2 and ISO 27001 with a vCISO, Not a Full Security Team
SaaS founders facing enterprise deal security requirements can achieve SOC 2 or ISO 27001 compliance efficiently using a vCISO, avoiding the cost and time of building an in-house security team. A vCISO provides expert guidance, strategy, and audit support.
ReadBuilt for the frameworks you are audited against
Find out what an attacker can already see.
Verify you own the domain and we will run the same engine we point at a client on day one. No call, no obligation - the findings are yours either way.